
Case Study
A CPA Firm That Began With a Hesitant First Conversation and a Penetration Test.
A 30-year accounting practice that engaged us after a third-party penetration test showed gaps it could not see from the inside.
CPA firm · New Jersey and New York
The Client
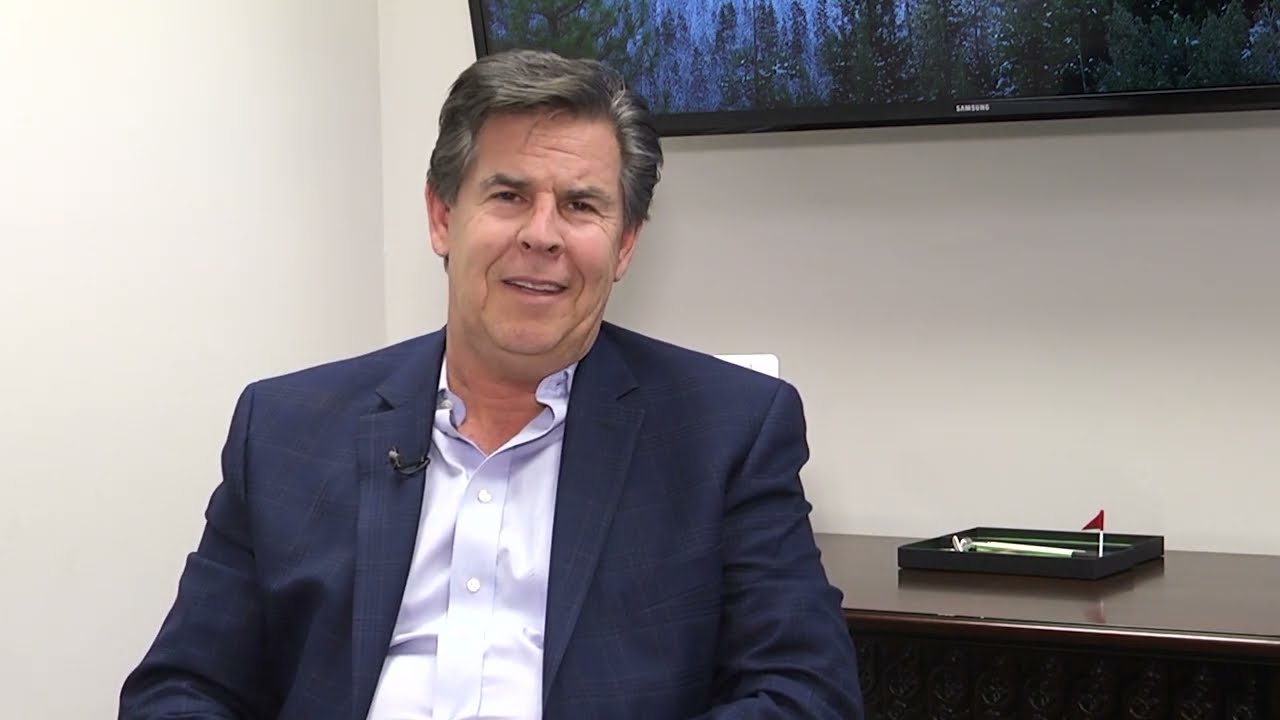
John Geantasio is a licensed CPA in New Jersey and New York with more than 30 years in accounting and taxation. His firm handles tax returns, Social Security numbers, banking details and confidential corporate records.
The Challenge
John was hesitant at first, like many CPAs, and was not convinced his firm was at meaningful risk. A third-party penetration test showed that even reputable firms have hidden vulnerabilities.
What We Did
“The testing was so easy on my side, and the level of experience and service was exceptional. I am now a happy customer and feel more secure knowing my clients' data is protected by a team that truly understands what's at stake.”
Talk It Through in 30 Minutes.
Pick a time. Tell us what you protect and who asks about it.
Looking for CMMC? Our Compliance Division, Capital Cyber Compliance, delivers it.